Modern Applications Have Changed. Has Your Pentest Methodology?
Modern applications are no longer built from scratch. Today, it is common for applications
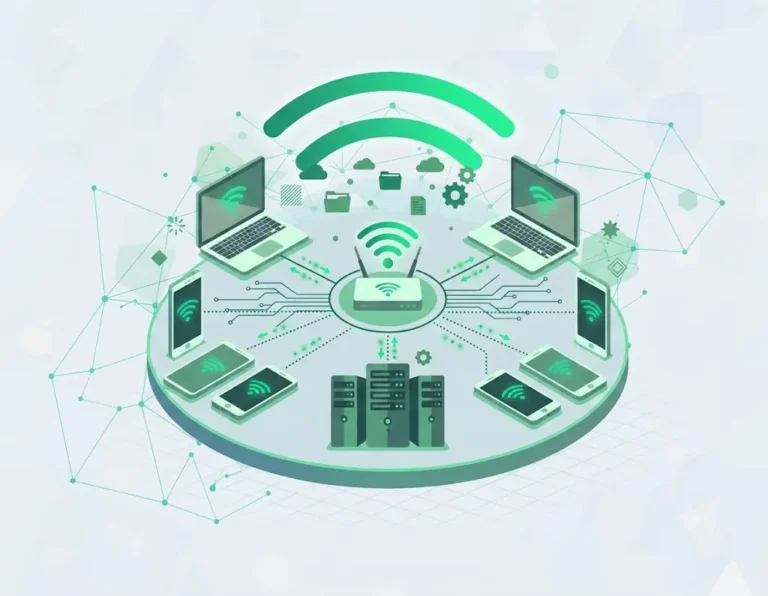
A Wireless Penetration Test, also known as a Wi-Fi Pentest or Wireless Security Assessment, simulates real-world attacks against your organisation’s wireless network to identify vulnerabilities before they can be exploited.
Unlike traditional network penetration testing, which focuses on wired infrastructure such as firewalls, routers, switches and servers, wireless penetration testing assesses the security of Wi-Fi networks and radio-based communications that extend beyond the physical boundaries of your premises.
Because attackers only need to be within wireless range, Wi-Fi penetration tests are typically performed on-site to simulate realistic attack scenarios. This helps determine whether an attacker could gain unauthorised access, intercept sensitive data, capture credentials or use the wireless network as a pathway into internal systems.
Guest WiFi networks are used by a high volume of temporary users everyday. Attackers can connect to these networks undetected and attempt to bypass security controls, access internal systems, or steal sensitive data if network segmentation and client isolation are weak or disabled.
Corporate WiFi networks often provide direct access to internal systems and sensitive business data. Weak authentication, poor segmentation, or misconfigured wireless security controls may allow attackers within radio range to gain unauthorised access or pivot deeper into the corporate network
When multiple organisations share the same wireless environment, poor isolation between networks can create cross-tenant risks. Without proper segmentation and security testing, attackers may exploit vulnerabilities to access another organisation’s data or systems operating within the same WiFi infrastructure.
A user on Guest or Free WiFi pivots into sensitive corporate subnets eg. HR, Finance or R&D, proving the network is not segmented to stop adversaries.
Without wireless isolation, every device on the same WiFi can freely scan, discover and launch attack against devices on the same subnet
MAC address spoofing clones an already authenticated device, tricking the router into granting full access, bypassing the captive portal
Management interfaces eg. SSH, admin or database consoles are reachable from general wireless network, exposing infrastructure to attacks
Unencrypted cleartext protocols eg. HTTP, FTP, inside the wireless tunnel allow attackers to capture credentials and sensitive corporate data directly from the air

Licensed by CSA under CSRO and onboarded as a CISOaaS VAPT provider by CSA, ensuring accountability and regulatory compliance.
Licence No CS/PTS/C-202606-336

Our consultants hold industry certifications including CREST, CISSP and AWS, backed by over 20 years of practical cybersecurity and infrastructure experience.
Receive detailed findings with reproducible POCs for effective remediation. Our reports also document existing security strengths, providing official attestations for your auditors.
Yes. Wi-Fi penetration testing requires physical proximity to your wireless environment. Our testers conduct the assessment on-site using specialised wireless hardware to accurately simulate a real attacker operating from within or near your premises. Remote wireless testing is not feasible and would not reflect realistic attack conditions.
Black Box testing simulates an external attacker with no prior knowledge — ideal for testing whether hidden networks can be found, guest portals bypassed, or encryption cracked from the lobby.
Grey Box testing simulates a compromised guest or insider with basic access, uncovering deeper flaws like whether a guest can pivot into the corporate network.
Many clients run both for complete coverage. VAPT is a critical component for regulatory compliance. It serves as documented proof of due diligence, providing the necessary reassurance to authorities, auditors, and stakeholders that your organization is committed to maintaining a robust and resilient security environment.
A network pentest focuses on your wired infrastructure — servers, firewalls, and Active Directory. A Wi-Fi pentest specifically targets your wireless access points, SSIDs, encryption, and the paths an attacker could use to gain a foothold wirelessly before pivoting into the wired environment. For comprehensive coverage, both are recommended.
Minimally. We define clear rules of engagement with your IT team before testing begins. Certain simulations — such as deauthentication testing — may cause brief disconnections on targeted test devices, but these are scheduled and controlled to avoid impacting production users or business-critical operations.
Typically, a wireless penetration test takes 2 to 5 business days per location, depending on the physical size of your facility and network complexity.
To ensure an accurate assessment, our execution depends on two critical factors:
Peak Operational Testing: Testing must be conducted on-site during active business hours when your staff are on the network. This allows us to accurately map active or hidden SSIDs, measure signal perimeter leakage, and observe real-time traffic volumes under realistic conditions.
Targeted Traffic Capture: Intercepting the specific cryptographic handshakes required for simulated exploitation relies entirely on active user behavior. Depending on your network’s activity patterns, our team may conduct multiple targeted site visits across different shifts to capture the data needed to thoroughly test your defenses.
Our report consists of:
Modern applications are no longer built from scratch. Today, it is common for applications
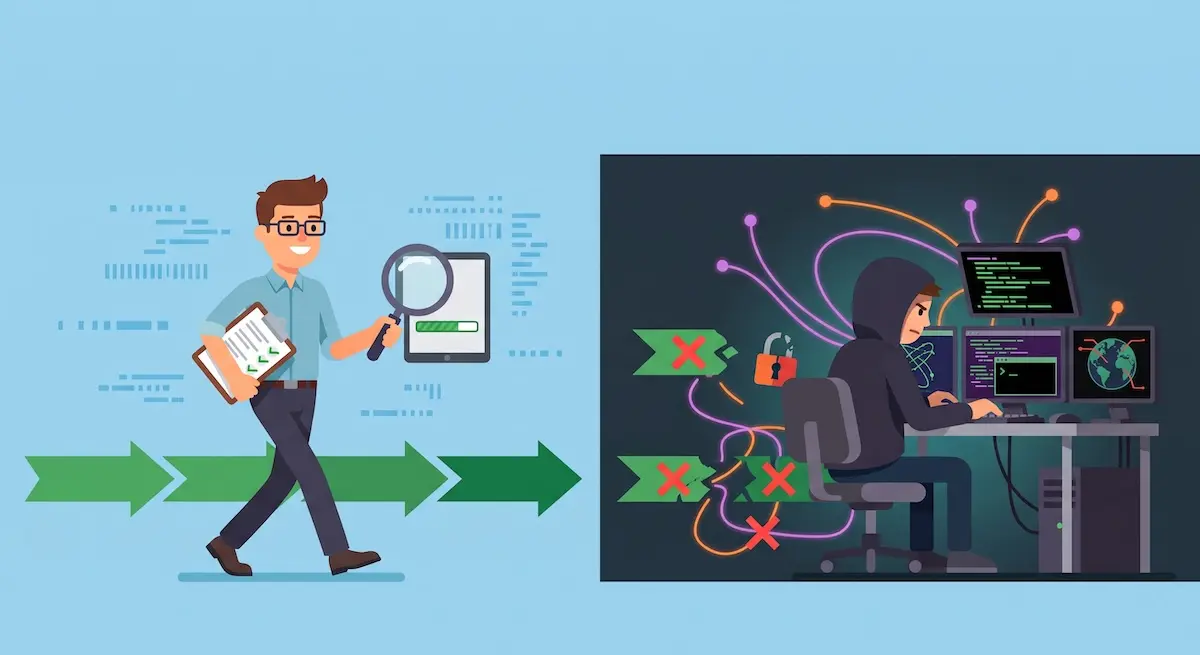
“But we already implemented that.” This is something we occasionally hear after reporting a
Single Page Applications (SPAs) have become increasingly popular for modern web applications. Frameworks such