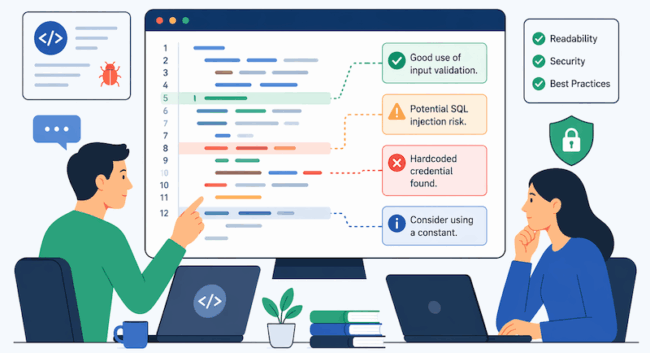
Code Review – a Necessity in the Age of AI

For many organisations, code review has traditionally been seen as something “nice to have.” A practice reserved for: Large enterprises Government projects High-assurance systems For everyone else—especially fast-moving teams—it was often skipped in favour of speed. That trade-off is becoming increasingly dangerous. AI Has Changed How Vulnerabilities Are Found The way vulnerabilities are discovered today…

The CVSS Trap: Why “Low” Vulnerabilities Still Matter in Penetration Testing

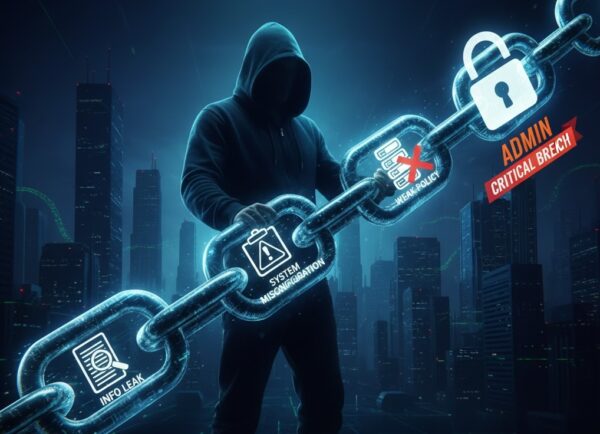
Many organisations prioritise patching only High and Critical vulnerabilities. At first glance, this seems practical — limited resources, endless findings, and urgent operational demands mean security teams must draw the line somewhere. Unfortunately, this mindset creates a dangerous blind spot. In real-world attacks, breaches rarely result from a single critical vulnerability. Instead, attackers systematically chain…

Security Through Obscurity: Flawed Strategy or Layered Defense?

In cybersecurity, Security Through Obscurity (STO) is the notion that hiding system details—like code, architecture, or configurations—can keep attackers at bay. At best, it’s a temporary deterrent. At worst, it’s a dangerous illusion that collapsed defenses once the secret is out. Recent events around Microsoft’s tightening of its Active Protections Program (MAPP) highlight why obscurity…