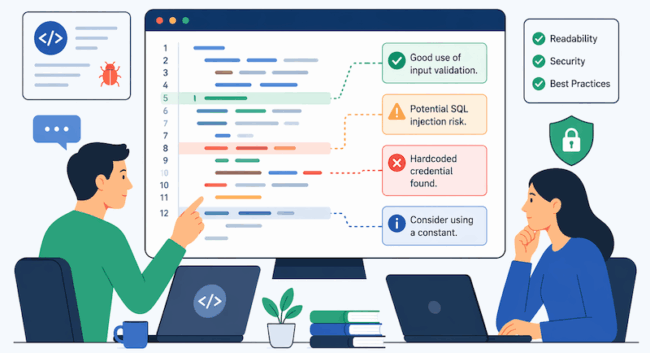
Code Review – a Necessity in the Age of AI

For many organisations, code review has traditionally been seen as something “nice to have.” A practice reserved for: Large enterprises Government projects High-assurance systems For everyone else—especially fast-moving teams—it was often skipped in favour of speed. That trade-off is becoming increasingly dangerous. AI Has Changed How Vulnerabilities Are Found The way vulnerabilities are discovered today…

The CVSS Trap: Why “Low” Vulnerabilities Still Matter in Penetration Testing

Many organisations prioritise patching only High and Critical vulnerabilities. At first glance, this seems practical — limited resources, endless findings, and urgent operational demands mean security teams must draw the line somewhere. Unfortunately, this mindset creates a dangerous blind spot. In real-world attacks, breaches rarely result from a single critical vulnerability. Instead, attackers systematically chain…

Cybersecurity Requirements M&E Vendors Must Meet for CII Projects

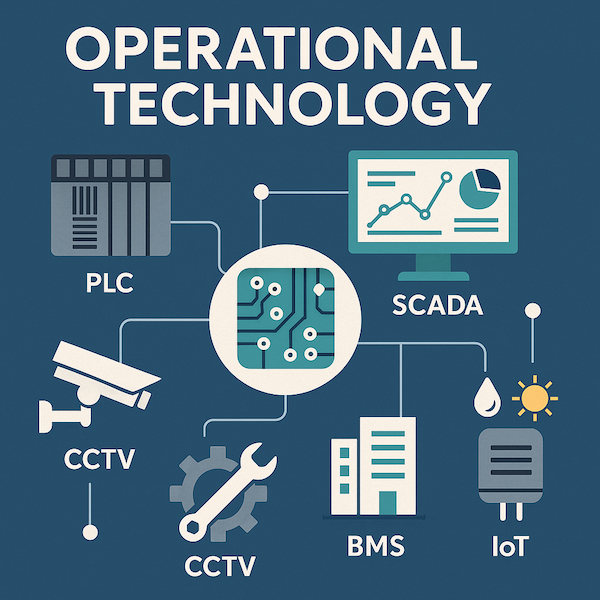
Mechanical & Electrical (M&E) vendors supporting Singapore Government projects increasingly operate at the intersection of Operational Technology (OT) and Information Technology (IT). Systems such as Building Management Systems (BMS), CCTV, access control, lifts, sensors, and industrial controllers are no longer isolated mechanical components — they are networked, IP-based, and cyber-exposed. To manage these risks, Government…